Are you frustrated and struggling with your WIFI or edge network security? Experiencing any of the following frustrations?
- My IT or IT Risk budget is too small, and we can’t afford the right cyber security tools to test, manage and maintain the WIFI / edge network
- My clients, vendors, partners or regulators require me to comply with specific standards, cyber security and cyber resilience requirements and/or incoming regulations for the joint standards
- I need to supply reports to stakeholders and/or attest to my WIFI or Edge Network controls in third party risk questionnaires / assessments
- I need to have network documented but it takes too long to draw network topology diagrams and keep them updated!
- My tools are too complex, or they don’t provide the functionality that we require
- We can’t afford to hire consultants to help us every time we have a network issue or need to troubleshoot
- The auditors keep telling us we have to test for vulnerabilities at Head Office and at the branches, look for rogue and/or unauthorised devices or software, monitor the WIFI network etc.
- My cyber team / information security team keep telling me we may get hacked at any moment and we need to do more regular WIFI penetration testing. But is simply too expensive to outsource and hire consultants!

Sound familiar? we may be able to help. Looking for a comprehensive and affordable tool that maps back to CIS, NIST and ISO 27001 frameworks, evolving cybersecurity and cyber resilience regulations such as the joint standards.
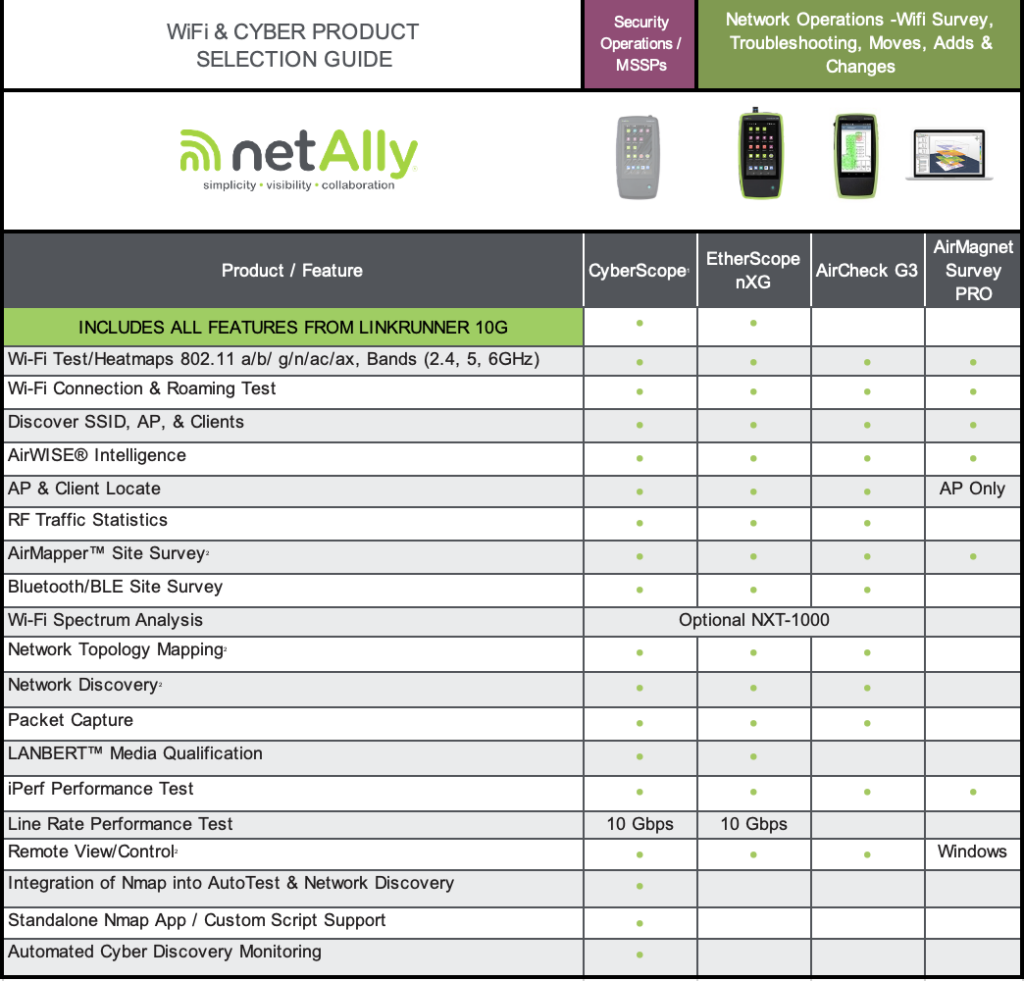
The Cyber Scope is a valuable tool in helping to keep your Network and IT environment secure and assists with the documentation of network topology and reports to demonstrate governance, risk and compliance (GRC requirements) and best practices to your internal and external stakeholders.
| No | CIS Control | ISO 27001 Control | NIST Control |
| 1 | Control 1 – Inventory and Control of Enterprise Assets | Inventory of information and other associated assetsManagement of technical vulnerabilities | System Component InventorySystem Component Inventory | Updates During Installation and RemovalSystem InventorySystem Component Inventory | Automated Unauthorized Component DetectionSystem Monitoring |
| 2 | Control 4 – Secure Configuration of Enterprise Assets and Software | Configuration Management | Nonlocal MaintenanceConfiguration SettingsLeast FunctionalitySecure Name/address Resolution Service (authoritative Source)Secure Name/address Resolution Service (recursive or Caching Resolver)Architecture and Provisioning for Name/address Resolution Service |
| 3 | Control 7 -Continuous Vulnerability Management | Management of Technical Vulnerabilities | Vulnerability Monitoring and Scanning |
| 4 | Control 12 – Network Infrastructure Management | Segregation of NetworksSecurity of Network Services | System Component Inventory | Updates During Installation and RemovalSecurity and Privacy ArchitecturesEnterprise ArchitectureSecurity and Privacy Engineering PrinciplesLeast FunctionalityAlternate Storage SiteAlternate Processing SiteBoundary ProtectionConfiguration SettingsSession AuthenticitySystem Inventory- Wireless Access |
| 5 | Control 13 – Network Monitoring and Defense | Management of Technical Vulnerabilities | Configuration SettingsLeast Functionality |
| 6 | Control 18 – Penetration Testing | Management of Technical Vulnerabilities |